
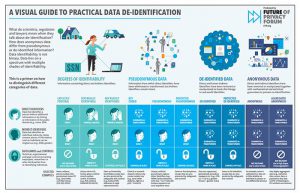
One key method for ensuring privacy while processing large amounts of data is de-identification. De-identified data refers to data through which a link to a particular individual cannot be established. This often involves “scrubbing” the identifiable elements of personal data, making it “safe” in privacy terms while attempting to retain its commercial and scientific value.
In the era of big data, the debate over the definition of personal information, de-identification and re-identification has never been more important. Privacy regimes often rely on data being considered Personal in order to require the application of privacy rights and protections. Data that is anonymous is considered free of privacy risk and available for public use.
Yet much data that is collected and used exists somewhere on a spectrum between these stages. FPF’s De-ID Project has examined practical frameworks for applying privacy restrictions to data based on the nature of data that is collected, the risks of de-identification, and the additional legal and administrative protections that may be applied.
Innovation and Data Privacy Are Not Natural Enemies: Insights from Korea’s Experience
The following is a guest post to the FPF blog authored by Dr. Haksoo Ko, Professor at Seoul National University School of Law, FPF Senior Fellow and former Chairperson of South Korea’s Personal Information Protection Commission. The guest post reflects the opinion of the author only and does not necessarily reflect the position or views […]
FPF Year in Review 2025
Co-authored by FPF Communications Intern Celeste Valentino with contributions from FPF Global Communications Manager Joana Bala This year, FPF continued to broaden its footprint across priority areas of data governance, further expanding activities across a range of cross-sector topics, including AI, Youth, Conflict of Laws, AgeTech (seniors), and Cyber-Security. We have engaged extensively at the local […]
Chile’s New Data Protection Law: Context, Overview, and Key Takeaways
On August 26, 2024, the Chilean Congress approved Law 21.719, on the Protection of Personal Data (“LPPD”) after eight years of legislative debate. The legislation was published on December 13, 2024, and will become fully effective twenty-four months after that date (in December 2026). The LPPD was introduced in the Senate in 2017 to replace […]

OAIC’s Dual AI Guidelines Set New Standards for Privacy Protection in Australia
On 21 October 2024, the Office of the Australian Privacy Commissioner (OAIC) released two sets of guidelines (collectively, “Guidelines”), one for developing and training generative AI systems and the other one for deploying commercially available “AI products”. This marks a shift in OAIC’s regulatory approach from enforcement-focused oversight to proactive guidance. The Guidelines establish rigorous […]
The North Star State Joins the State Privacy Law Constellation
On May 19, 2024, the Minnesota Legislature passed HF 4757, an omnibus budget bill that includes the Minnesota Consumer Data Privacy Act (MNCDPA). The bill now heads to Governor Walz for signature. Developed by State Representative Steve Elkins over nearly five years and multiple legislative sessions, the MNCDPA is among the strongest iterations of the […]
The DNA of Genetic Privacy Legislation: Montana, Tennessee, Texas, and Virginia Enter 2024 with New Genetic Privacy Laws Incorporating FPF’s Best Practices
In 2023, four states enacted new genetic privacy laws regulating direct-to-consumer genetic testing companies. This blog post provides details on what these new laws cover and how they compare to FPF’s widely-adopted Best Practices for Consumer Genetic Testing Services. Genetic privacy has been under increasing scrutiny at the state and federal levels, and regulators are […]
Optum & The Mayo Clinic Win the 2022 Award for Research Data Stewardship
Author: Randy Cantz, U.S. Policy Intern, Ethics and Data in Research and former Communications Intern at FPF On Wednesday, May 10, 2023, the Future of Privacy Forum (FPF) honored representatives from Optum and the Mayo Clinic for their outstanding corporate-academic research data-sharing partnership at the 3rd annual Awards for Research Data Stewardship. The awards honor […]
What to Expect from the Review of Australia’s Privacy Act
The author thanks Anna Johnston and Alex Kotova (Salinger Privacy) for their review and comments and Gabriela Zanfir-Fortuna, Josh Lee Kok Thong, Lee Matheson, and Isabella Perera (FPF) for their support with editing this post. On February 16, 2023, Australia’s Attorney-General’s Department (AGD) released a final report (Review Report) on its multi-year review of Australia’s […]
The African Union’s Data Policy Framework: Context, Key Takeaways, and Implications for Data Protection on the Continent
Authors: Mercy King’ori, Ulric Quee, Hunter Dorwart On July 28, 2022, the African Union (AU) released its Data Policy Framework (Framework) following extensive multi-stakeholder engagements. The Framework aims to provide a multi-year blueprint for how the AU will accomplish its goals for Africa’s digital economy. It also sets forth the AU’s vision, scope, and priorities […]
“Are crumbles all that remains of the cookies?” A conversation on the future of ad tech at the Nordic Privacy Arena 2021
On September 27 and 28, 2021, the Swedish Data Protection Forum (Forum för Dataskydd) hosted the 2021 edition of the Nordic Privacy Arena (“Operationalising Data Privacy – Challenges, best practices, and success stories”) in Stockholm, Sweden. This hybrid event brought together privacy practitioners, watchdogs, and academics to debate some of the most pressing issues regarding […]