
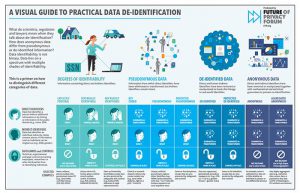
One key method for ensuring privacy while processing large amounts of data is de-identification. De-identified data refers to data through which a link to a particular individual cannot be established. This often involves “scrubbing” the identifiable elements of personal data, making it “safe” in privacy terms while attempting to retain its commercial and scientific value.
In the era of big data, the debate over the definition of personal information, de-identification and re-identification has never been more important. Privacy regimes often rely on data being considered Personal in order to require the application of privacy rights and protections. Data that is anonymous is considered free of privacy risk and available for public use.
Yet much data that is collected and used exists somewhere on a spectrum between these stages. FPF’s De-ID Project has examined practical frameworks for applying privacy restrictions to data based on the nature of data that is collected, the risks of de-identification, and the additional legal and administrative protections that may be applied.
No Silver Bullet, But a Silver Lining? PETs and International Data Transfers
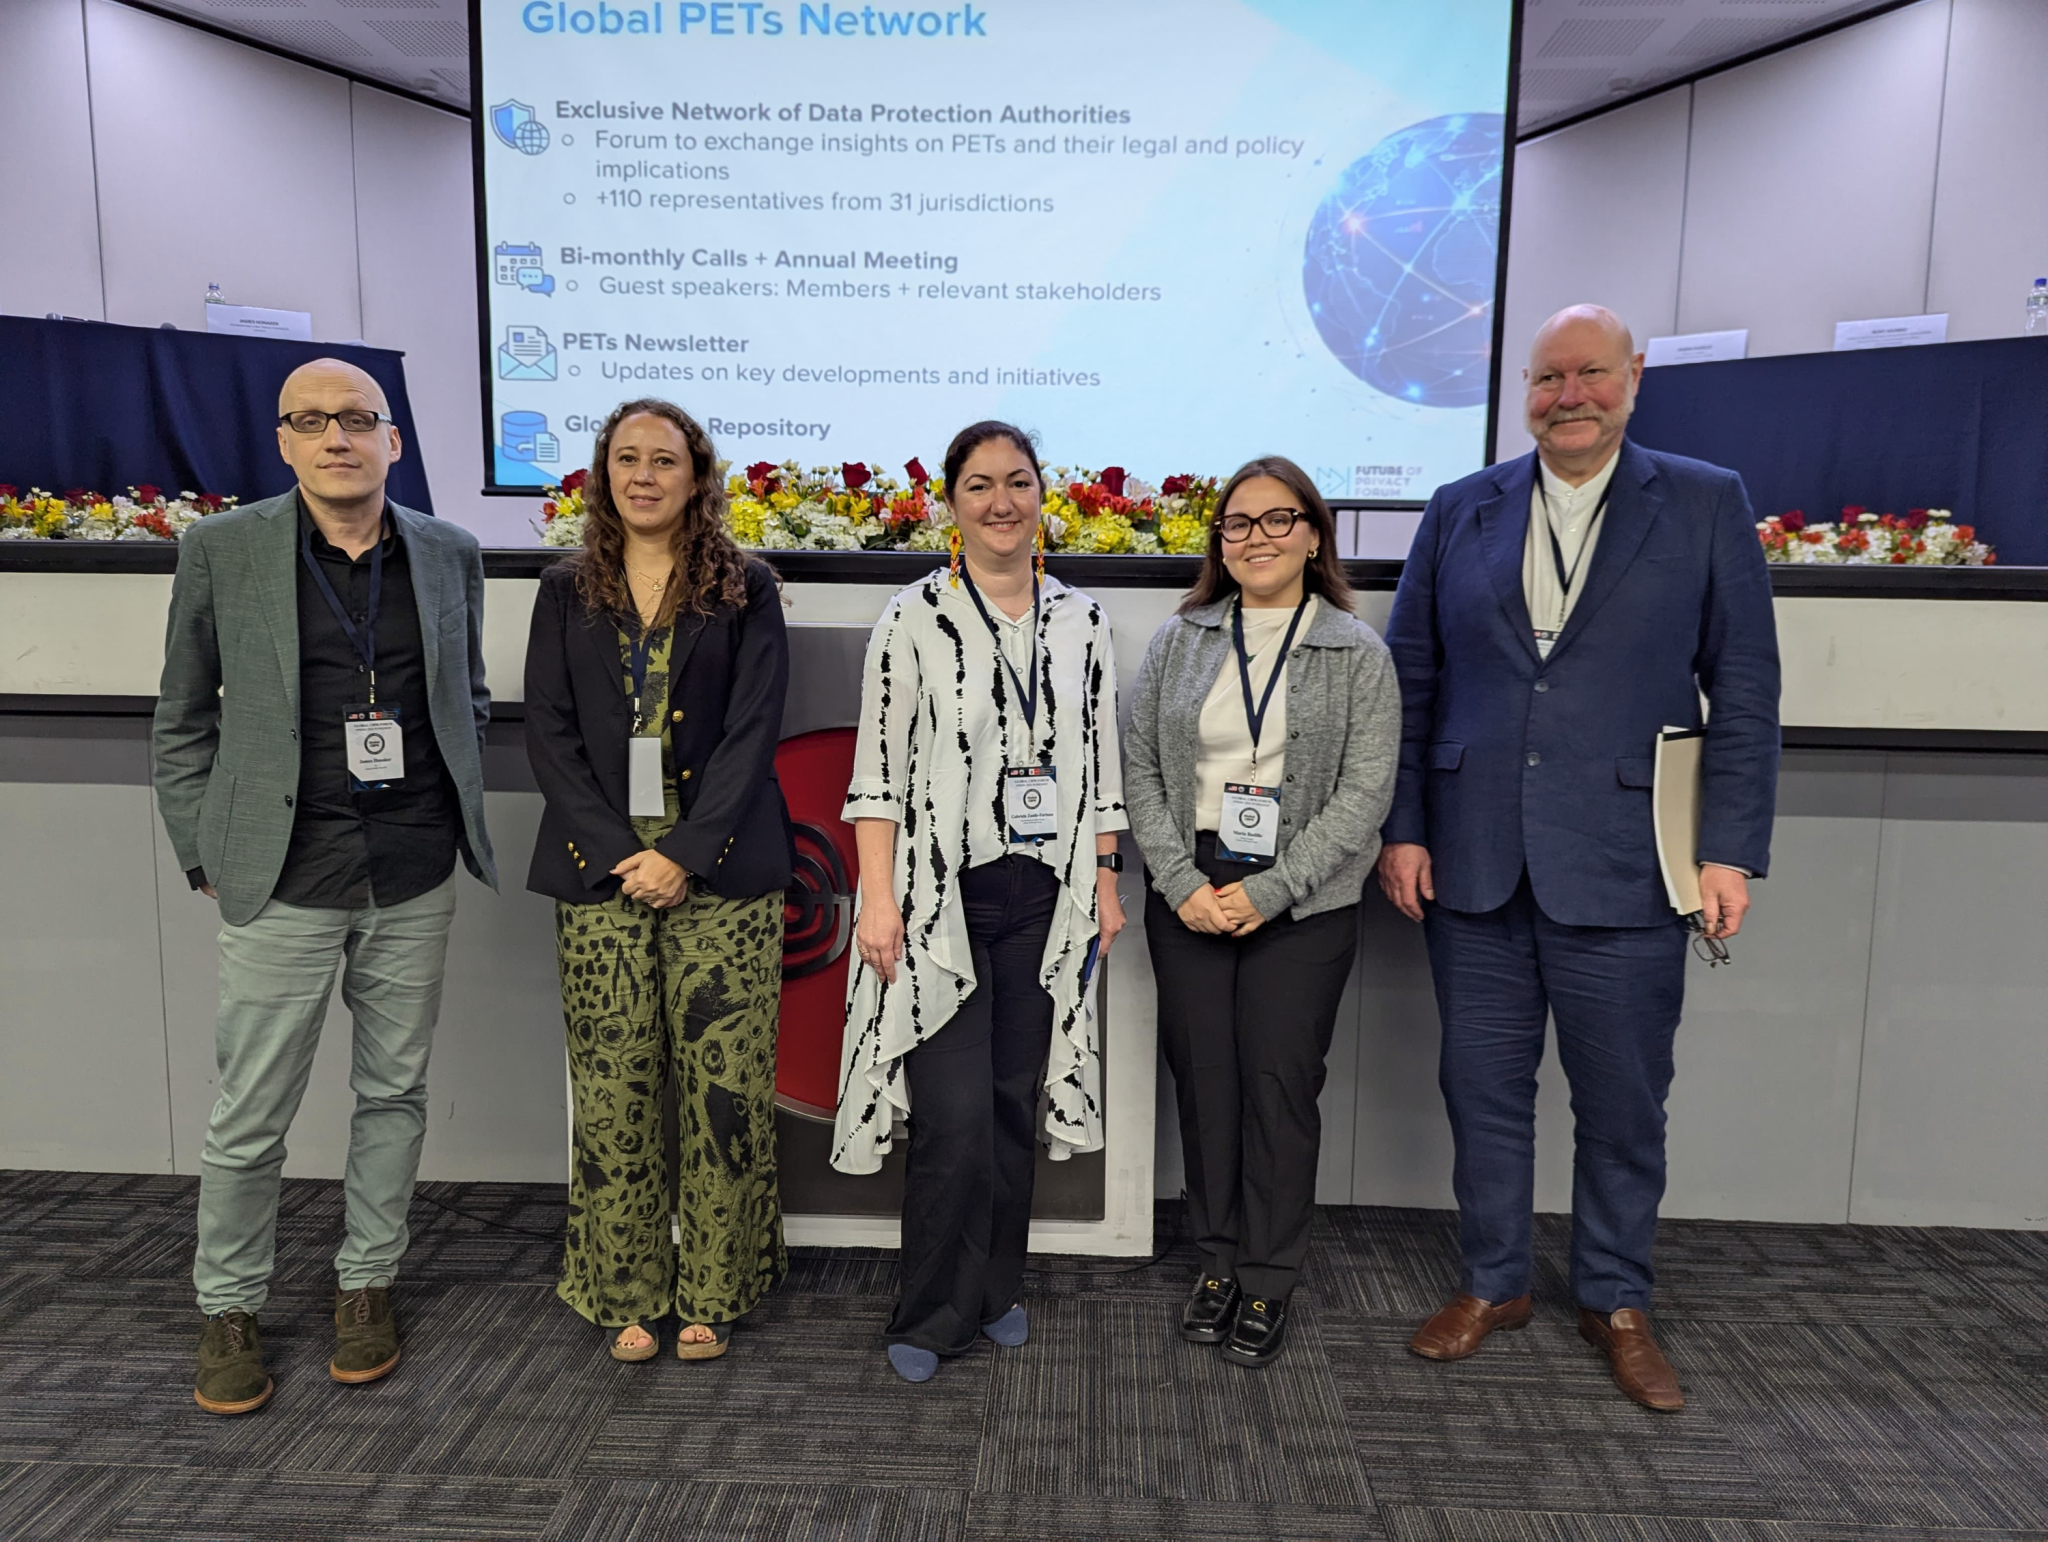
Is there a role for Privacy Enhancing Technologies (PETs) to play in the context of international data transfers? The answer to this question could be one of the keys to unlock trusted cross-border data flows at scale in the age of AI. This was the topic explored in a session organized by the Future of […]
2026: A Year at the Crossroads for Global Data Protection and Privacy
There are three forces twirling and swirling to create a perfect storm for global data protection and privacy this year: the surprise reopening of the General Data Protection Regulation (GDPR) which will largely play out in Brussels over the following months, the complexity and velocity of AI developments, and the push and pull over the […]
FPF Year in Review 2025
Co-authored by FPF Communications Intern Celeste Valentino with contributions from FPF Global Communications Manager Joana Bala This year, FPF continued to broaden its footprint across priority areas of data governance, further expanding activities across a range of cross-sector topics, including AI, Youth, Conflict of Laws, AgeTech (seniors), and Cyber-Security. We have engaged extensively at the local […]
Rethinking Personal Data: The CJEU’s Contextual Turn in EDPS vs. SRB
Author: Cédric Burton The following is a guest post to the FPF blog authored by Cédric Burton, Partner and Global Co-Chair Data, Privacy and Cybersecurity, Wilson Sonsini Brussels. The guest post reflects the opinion of the author only and does not necessarily reflect the position or views of FPF and our stakeholder communities. FPF provides […]
Chile’s New Data Protection Law: Context, Overview, and Key Takeaways
On August 26, 2024, the Chilean Congress approved Law 21.719, on the Protection of Personal Data (“LPPD”) after eight years of legislative debate. The legislation was published on December 13, 2024, and will become fully effective twenty-four months after that date (in December 2026). The LPPD was introduced in the Senate in 2017 to replace […]
Twelve Privacy Investments for Your Company for a Stronger 2025
FPF has put together a list of Twelve Privacy Investments for Your Company for a Stronger 2025 that reflects on new perspectives on the work that privacy teams do at their organizations. We hope there is something here that’s useful where you work, and we’d love to hear other ideas and feedback. Privacy Investments for Your […]

OAIC’s Dual AI Guidelines Set New Standards for Privacy Protection in Australia
On 21 October 2024, the Office of the Australian Privacy Commissioner (OAIC) released two sets of guidelines (collectively, “Guidelines”), one for developing and training generative AI systems and the other one for deploying commercially available “AI products”. This marks a shift in OAIC’s regulatory approach from enforcement-focused oversight to proactive guidance. The Guidelines establish rigorous […]

NEW FPF REPORT: Confidential Computing and Privacy: Policy Implications of Trusted Execution Environments
Written by Judy Wang, FPF Communications Intern Today, the Future of Privacy Forum (FPF) published a paper on confidential computing, a privacy-enhancing technology (PET) that marks a significant shift in the trustworthiness and verifiability of data processing for the use cases it supports, including training and use of AI models. Confidential computing leverages two key […]
This Year’s Must-Read Privacy Papers to be Honored at Washington, D.C. Event
The Future of Privacy Forum’s 14th Annual Privacy Papers for Policymakers Award Recognizes Influential Privacy Research Today, the Future of Privacy Forum (FPF) — a global non-profit focused on data protection headquartered in Washington, D.C. — announced the winners of its 14th annual Privacy Papers for Policymakers (PPPM) Awards. The PPPM Awards recognize leading U.S. […]
What to Expect from the Review of Australia’s Privacy Act
The author thanks Anna Johnston and Alex Kotova (Salinger Privacy) for their review and comments and Gabriela Zanfir-Fortuna, Josh Lee Kok Thong, Lee Matheson, and Isabella Perera (FPF) for their support with editing this post. On February 16, 2023, Australia’s Attorney-General’s Department (AGD) released a final report (Review Report) on its multi-year review of Australia’s […]