Do you have an interesting perspective on Europe’s General Data Protection Regulation or insightful information about GDPR to share? IEEE Security and Privacy seeks articles from scholars and practitioners from various disciplines and countries to examine GDPR: A Year On. Successful submissions will address (among other topics) the GDPR’s:
• position at the intersection of law and technology;
• global impact;
• implications for global multinationals and for small and medium size enterprises;
• implementation by engineers, economists, and lawyers;
• potential macroeconomic and competitive impact; and
• effect on debates about ethics beyond the law.
Submissions are due by March 1, 2019, with publication in November/December, 2019. Articles should be understandable to a broad audience of people interested in security and privacy, and run between 4,900 to 7,200 words. IEEE’s website has more information about submission requirements, or you can email the guest editors at [email protected].
Guest editors for the special issue are:
• Omer Tene, IAPP and FPF (lead editor)
• Katrine Evans, Hayman Lawyers
• Bruno Gencarelli, European Commission
• Gabe Maldoff, Bird & Bird
• Gabriela Zanfir-Fortuna, FPF
FPF at 10: Envisioning the Future of Privacy
This year, Future of Privacy Forum is celebrating our tenth anniversary as a catalyst for privacy leadership and scholarship. In recognition of this milestone, we will host an anniversary celebration on April 30 and release a report on rising privacy issues. We also are publishing a series of blog posts over the next several weeks in which our policy experts will share their thoughts on FPF’s work over the past decade, the current privacy landscape, and their vision for the future of privacy.
Read the first post below with Jules Polonetsky’s Q&A and sign up for our mailing list to receive updates when new posts are published.
Q&A: Jules Polonetsky on the Future of Privacy
Jules Polonetsky has been CEO of the Future of Privacy Forum since its founding 10 years ago. He is uniquely suited to bring together privacy experts from industry, consumer advocacy and government. Before he joined FPF, Jules was the Chief Privacy Officer at AOL and DoubleClick, New York City Consumer Affairs Commissioner, a New York state legislator, a congressional staffer and an attorney.
As we observe its 10th Anniversary, how would you describe the idea behind the Future of Privacy Forum?
Our goal at the Future of Privacy Forum is to provide a roadmap on how our world can experience the benefits of data in a way that is ethical, moral, and that maintains our individual senses of self and autonomy.
There are so many areas where data holds opportunity to improve our health, safety, and happiness, but every one of those opportunities also is a source of great risks. We may come up with new medical advances by studying electronic health records but we need to do that in a manner that respects individual privacy. We want a world that is safer from things like terrorism but we don’t want government monitoring every email and phone call. We believe we can integrate privacy protections with responsible data use that will improve our lives.
So we convene experts from businesses, government, academia and civil society to get the best thinking and promote insightful research. We’ve also spurred industry to take actions with real-world impacts to protect consumer privacy. For example, the 300 companies that have taken the Student Privacy Pledge submit to legally enforceable obligations, such as not to sell students’ personal information. Likewise, companies that support FPF’s Privacy Best Practices for Consumer Genetic Testing Services agree to a set of standards for the collection and use of genetic data, like not sharing individual genetic data without express permission.
And we’re not just influencing industry practices. Our Open Data Risk Assessment used in Seattle and other cities helps government officials navigate the complex policy, technical, organizational and ethical standards that support privacy-protective open data programs.
How do you balance enthusiasm about innovative technology with an awareness that there can be pitfalls?
As a think tank director working with companies and advocates and government and foundations, I’m excited about the latest breakthroughs in technology. I’m also aware of the incredible consequences if we don’t put the right policies and structures and laws in place to make sure society benefits in a way that lifts us all up and takes us in a positive direction.
At FPF, we try to be at the center of the world of privacy. We work with companies to make sure when they use data, they are doing it in a responsible way. We also work with academics and civil society folks who worry that the government or companies could take us down an Orwellian path.
What are you looking for in potential privacy legislation from this Congress?
The White House, Congress, industry and civil society are increasingly in agreement about the need for comprehensive federal privacy legislation, so I hope a productive bill can be passed and signed into law. There are a few things I’ll be looking for in new legislation.
First, the rules should be technology neutral and cover every type of company and business model. Data is collected across platforms — on the web, on mobile, with wearables, smart home devices, and phone and facial tracking — and one clear set of rules is easiest for consumers to understand.
Legislation should recognize that data flows internationally, and move us closer to interoperability with Europe and other countries, while preserving room for new ideas and entrepreneurship.
Another foundational principle is fairness, which means using data only as people would reasonably expect and not using it in ways that have unjustified adverse effects. This concept is very similar to how the current FTC Act authorizes legal action against deceptive or unfair practices.
Also, any legislation should consider the increasingly sophisticated privacy tools that are emerging, including differential privacy to measure privacy risk, homomorphic encryption that can enable privacy safe data analysis, and many new privacy compliance tools that are helping companies better manage data. A law that will stand the test of time and successfully protect privacy rights while enabling valuable uses of data should include mechanisms to incentivize new privacy-friendly technology.
What is a cutting-edge privacy issue that you think will grow in importance over the next ten years?
The world of artificial intelligence and machine learning is fascinating and important. We’re just beginning to scratch the surface of the opportunities, but we’re also starting to understand what a dangerous and dark path the misuses of those types of data could lead to. There is a risk of being overly optimistic and not understanding that we could take ourselves to a place of no return.
I hope that in ten years – when FPF celebrates its 20th anniversary – we won’t be fixing ineffective rules and laws from this era. For example, the GDPR, if interpreted narrowly, could pose some challenges for AI and machine learning, since it specifies that personal data must be collected only for a specified purpose, and must be deleted or minimized when not needed for that purpose. For many machine learning processes today, large and representative data sets are required to power new models, to ensure accuracy and to avoid bias. As European regulators seek to advance trusted AI, ensuring the right balance here will be essential.
And as Congress considers a U.S. privacy framework, we will be advising policymakers on the ways that uses of data for machine learning and other innovations can be supported, when responsible safeguards are in place.
I’m looking forward to seeing the work of FPF’s AI and Machine Learning Working Group – and all of our program areas – evolve in the coming years!
Check back in coming weeks for more discussions with FPF policy experts and sign up for our mailing list to stay informed about important privacy issues.
FPF, EFPIA, and CIPL Workshop Report Now Available: "Can GDPR Work for Health Scientific Research?"
On October 22, 2018, the Future of Privacy Forum (FPF), the European Federation of Pharmaceutical Industries and Associations (EFPIA), and the Centre for Information Policy Leadership (CIPL) hosted a workshop in Brussels, “Can GDPR Work for Health Scientific Research?,” to discuss the processing of personal data for health scientific research purposes under the European Union’s General Data Protection Regulation (GDPR).
The use of health data in research, whether it arises in the course of hospital treatment or from personal management of care, has the potential to improve the lives of individuals, as well as transform health care systems and health-related science and innovation. Yet, at this moment, researchers and private and public stakeholders generally are facing difficulty in understanding how to comply with GDPR when processing personal data for health scientific research. Further, National Data Protection Authorities (DPAs), Health Authorities, and Ethical Committees are providing differing guidance on what should be the basis for processing special categories of personal data in scientific research, and the divergences are, if anything, widening.
The workshop highlighted multiple issues at the center of this challenge including:
The role of consent, legitimate interest, and other legal bases in the processing of health data for clinical trials and in the secondary use of health data for health scientific research purposes;
The relationship between the Clinical Trials Regulation and the GDPR in regards to personal data processing for clinical trials;
The lack of clarity surrounding institutional responsibility and the role of ethical committees; and
The wider issues of how we ensure that emerging data driven technologies like real-world evidence and artificial intelligence can be leveraged in compliance with GDPR to advance innovation and improvements in care.
Legal and regulatory harmonization of approaches to health data research will be critical to the advancement of digital health to improve care and health outcomes. The European Data Protection Board (EDPB) will play a key role in working with the privacy and public research sectors to ensure harmonized application of the GDPR and legal certainty, as well as to clarify the situation and reconcile the needs of research while maintaining the rights of individuals to exercise choice and understand how their data is being used.
FPF to Co-Host Student Privacy Bootcamp with Student Data Privacy Consortium (1/28)
FPF will be hosting a Student Privacy Bootcamp with the Student Data Privacy Consortium on January 28th at the Future of Education Technology Conference (FETC) in Orlando. The free interactive event will provide concrete guidance and practical data privacy suggestions that can be implemented as soon as participants return to their districts. Slots are limited, so register now!
When: Monday, January 28th from 8:30am-3:00pm
Where: FETC Conference, Orange County Convention Center, 9800 International Dr, Orlando, FL 32819
There has been no shortage of laws and policies in recent years attempting to address student privacy concerns. These reflect a growing recognition that student privacy must be addressed seriously. For school districts, implementing good privacy practices and complying with laws can be daunting.
FPF Director of Education Privacy and Policy Counsel Amelia Vance will be co-leading sessions on federal laws (FERPA, COPPA, and PPRA), state laws and trends, and resources for administrators. There will also be a session on privacy best practices from other districts and hands-on exercises for participants.
The bootcamp will equip participants with the tools they need to implement responsible privacy practices, no matter the size of their district.
Other speakers include Steve Smith, Founder of the Student Data Privacy Consortium and Chief Information Officer of Cambridge Public Schools, Michael Hawes, Director of Student Privacy at the U.S. Department of Education, and more.
For a complete agenda and registration, click here.
Please reach out to Tyler Park ([email protected]) with any questions.
We hope to see you there!
Digital Data Flows Masterclass: Emerging Technologies
Digital Data Flows Masterclass is a year-long educational program designed for regulators, policymakers, and staff seeking to better understand the data-driven technologies at the forefront of data protection law & policy. The program will feature experts on machine learning, biometrics, connected cars, facial recognition, online advertising, encryption, and other emerging technologies.
The year-long program includes eight planned sessions in 2018-19 (view as PDF):
John Verdi Featured in WTOP Story About Connected Consumer Tech
Vice President of Policy John Verdi was featured in a WTOP story about the privacy implications of popular consumer tech holiday gifts. He offered advice on adjusting the privacy settings of smartphones, tablets, connected toys, and other devices. Read more at WTOP.
FPF joins 14 other organizations to urge ED and the FTC to provide guidance on the intersection of COPPA and FERPA
In December 2017, the U.S. Department of Education and the Federal Trade Commission hosted the workshop, “Student Privacy and Ed Tech.” The workshop brought together a wide range of stakeholders interested in protecting student privacy, with speakers representing districts, companies, and advocates. Almost all participants agreed that more clarity is necessary on the Children’s Online Privacy Protection Act (COPPA) and Family Educational Rights and Privacy Act (FERPA) requirements. However, more than a year later, ED and the FTC have not yet provided that guidance.
This week, the Future of Privacy Forum joined 14 other organizations – groups representing education, business, and consumer advocates – to send a letter to the U.S. Department of Education and Federal Trade Commission urging them to provide additional guidance on the intersection of COPPA and FERPA.
A New Year’s Resolution For Your New Devices
A New Year’s Resolution For Your New Devices
Still thinking about your New Year’s resolutions? If so, the Future of Privacy Forum has a practical suggestion: Get to know the privacy implications of your new electronics. Early in the New Year, take a few moments to set up privacy features so you can be comfortable with how your personal data is collected, used and shared.
Here are some of this year’s hot electronics, the information they collect and what you can do to exert some control over how they use your data.
SMART TVS – Understand how to limit sharing data about what you watch.
Smart TVs connect to the Internet to allow users to access streaming video services (such as Netflix or Hulu), or other online media or entertainment, such as music, on-demand video, and web browsers. Almost all TVs on the market today are “smart” – and other devices can be purchased, at relatively small cost, to connect to a regular TV and enable certain video streaming services.
Smart TVs collect a lot of data about your viewing habits, and that information may be shared with companies other than the device manufacturer or connected apps. For example, some advertising companies buy viewing data and add it to detailed profiles that also include offline data, like spending patterns. The information in that profile may determine what ads you are served on your TV, or on other devices, like your phone.
Tip: Some TVs prompt you to make privacy choices when you first set them up. Other TVs ask for permissions when you try to use specific features that collect data. Either way, you should be able to visit the settings menu at any time to review or change your preferences.
Tip: If you have the option to set up automatic software updates, do it. That will increase your security and improve the performance of the TV.
VOICE ASSISTANTS – Learn how to manage audio recordings.
Voice assistants, often called smart speakers, offer an amazing amount of information; your wish is its command. They also record a lot of information. Most of these devices are voice or speech-enabled, meaning that they use microphones to detect a certain “wake phrase,” but do not activate and begin recording (and sending information) until they hear that phrase. Most devices keep audio recordings of your commands so they can get better at recognizing your voice over time.
Tip: You can delete recordings of your voice commands or searches by logging into your account and managing your data history.
Tip: If you want the device to be responsive at all times, then it will probably pick up snippets of other noises in the room. Some devices may even occasionally activate by accident – for instance, if the device thought something you said was the “wake phrase.” Having a particularly sensitive conversation? Many voice assistants have a hard “mute” switch to turn it off.
WEARABLE TECH – Understand whether the app shares your health or location data.
Whether it’s a smart watch, a health monitor or an item of clothing, wearable tech is increasingly popular. Lots of wearable tech monitors your health or fitness, but unless it was prescribed by a health professional, it’s probably not covered by the strict privacy rules under the Health Insurance Portability and Accountability Act (HIPAA). Most wearables connect with an app, some of which share user information in unexpected ways. For example, some track a user’s location all the time and share that information with third parties.
Tip: You should check the app’s privacy practices and use the settings menu on your device to change default settings that you don’t like. It should only take a couple of clicks to prevent an app from collecting location data. Of course, if you want access to that data yourself, you have to let the app collect it – but you may be able to control privacy settings to prevent other uses or sharing.
CONSUMER GENETIC TESTS – Check the company’s privacy practices before you buy.
Genetic tests provide families with fascinating information about their heritage, and they also involve very sensitive personal information. Genetic data can be used to identify risk for future medical conditions, contain unexpected information that could be unsettling, or reveal sensitive information about the test taker’s family members.
Tip: Learn how a genetic testing company will protect or use your information before you buy.
Companies in the consumer genetic testing industry worked with the Future of Privacy to develop privacy and data principles. Here are some of the promises made by companies that endorsed FPF’s best practices:
The company should always obtain your consent before sharing your personal genetic data with any third parties.
The company should tell you how long it will keep your genetic data, and whether it will destroy your biological sample if you choose.
The company should tell you if it requires a court order or subpoena before sharing genetic data with the government.
The company should tell you whether it will limit marketing based on your genetic data, and how.
CONNECTED TOYS – Be aware of the data they may collect.
If you’ve got kids, they may have new connected toys that respond to voice commands, link to an app, or have to be set up using an online account. Although electronics and data processing can create great experiences for kids, toys that connect to the Internet raise concerns about what kind of data is collected from children, how that data is handled, and whether the device itself is secure.
Tip: Know whether the toy connects to the Internet. Many “smart toys” can perform sophisticated tasks using hardware on the toy but are not connected to the internet. If the toy is connected, it is usually through an app. Be sure to check the privacy settings on the app as well as the device.
Tip: If the toy gives you an option to reset the default password for accessing the toy via the app, do it. If you keep the default password – or there is no password – anyone in the vicinity of the toy can control it.
New Year’s Day is a great time to invest a few minutes with your new device’s privacy settings. If you do, you’re less likely to experience a data use disappointment in the future.
New FPF Study Documents More Than 150 European Companies Participating in the EU-US Data Transfer Mechanism
New FPF Study Documents More Than 150 European Companies Participating in the EU-US Data Transfer Mechanism
EU Companies’ Participation Grew by One Third Over the Past Year
By Jeremy Greenberg
Yesterday, the European Commission published its second annual review of the EU-U.S. Privacy Shield, finding that “the U.S. continues to ensure an adequate level of protection for personal data transferred under the Privacy Shield from the EU to participating companies in the U.S.” The decision preserves a key data transfer agreement, supporting transatlantic trade and ensuring meaningful privacy safeguards for consumers. It is also good news for EU employees and companies, many of whom rely on the agreement to retain and pay staff. The Commission’s review noted a key next step to support the Privacy Shield arrangement – urging the U.S. government to appoint a permanent Ombudsperson by the end of February 2019.
The Future of Privacy Forum conducted a study of the companies enrolled in the US-EU Privacy Shield program and determined that 152 European headquartered companies are active Privacy Shield Participants. This number is up from the 114 EU companies that were active Privacy Shield Participants last year. These European companies rely on the program to transfer data to their US subsidiaries or to essential vendors that support their business needs.
FPF also found that more than 3,700 companies have signed up for Privacy Shield – a nearly 70% increase in the number of participants from last year.
Leading EU companies that rely on Privacy Shield include:
ABB, Swiss electrical equipment company
Agfa, Belgian digital imaging and IT solutions company
CNH Industrial America, Dutch capital goods company
Fiat Chrysler, Italian global auto maker
HID Global, Swedish security company
Ingersoll-Rand, Irish globally diversified industrial company
Kodak Alaris, British photo retail and products company
Lidl Stiftung, German grocery market chain
Logitech, Swiss personal computer and mobile peripheral company
NCS Pearson, British education assessment and publishing company
P3, German management consultancy company
Reckitt Benckiser, British consumer goods company
RELX, British and Dutch information and analytics company
TE Connectivity, Swiss consumer electronics company
Telefónica, Spanish mobile network provider
WorkWave, Swedish software company
FPF research also determined that more than 1,150 companies, nearly a third of the total number analyzed, use Privacy Shield to process their human resources data. Inhibiting the flow of HR data between the US and EU would mean delays for EU citizens receiving their paychecks, or a decline in global hiring by US companies. Therefore, employees win when the Privacy Shield is maintained and grows.
The research identified 152 Privacy Shield companies headquartered or co-headquartered in Europe. This is a conservative estimate of companies that rely on the Privacy Shield framework – FPF staff did not include global companies that have major European offices but are headquartered elsewhere. The 152 companies include some of Europe’s largest and most innovative employers, doing business across a wide range of industries and countries. EU-headquartered firms and major EU offices of global firms depend on the Privacy Shield program so that their related US entities can effectively exchange data for research, to improve products, to pay employees and to serve customers. Given the importance of this mechanism to companies and consumers on both sides of the Atlantic, FPF is pleased that the Privacy Shield arrangement has been preserved and urges the U.S. government to quickly appoint a permanent Ombudsperson at the U.S. State Department.
Methodology:
FPF staff recorded a list of 3,703 active Privacy Shield companies as of September 2018 from https://www.privacyshield.gov.
FPF staff performed a web search for each current company by name, checking the location of the company’s headquarters on a combination of public databases such as LinkedIn, CrunchBase, Bloomberg, and companies’ own websites.
A company that listed its headquarters in an EU member state or in Switzerland was counted as a match; companies that merely had a prominent EU office or were founded in an EU member state were not counted.
152 total EU-headquartered companies were identified using this method.
FPF Releases Guide to Disclosing Information During School Emergencies
In Blog, FPF Expert Notes School Safety Report “Offers Little Guidance” on Privacy
WASHINGTON, DC – The Future of Privacy Forum released a guide to help school officials understand their ability under the law to share information about students in an emergency situation. The primary federal student privacy law, the Family Educational Rights and Privacy Act (FERPA), allows for exceptions to its general requirement that parents must approve information sharing during emergencies, including natural disasters, health crises, terrorist threats or active shootings. The guide explains:
schools’ obligations
opportunities for discretion under the law
to whom schools can disclose information,
what can be disclosed
limits on schools’ risk of liability.
FPF also published a blog post by Sara Collins, Tyler Park, and Amelia Vance of FPF’s Education Privacy Project, reviewing the very limited discussion of privacy issues in the Federal Commission on School Safety report released yesterday. While the report does include some information on acceptable data sharing during an emergency, it does not address how to implement security measures while including appropriate privacy protections. For example, the report recommends the use of “appropriate systems to monitor social media and mechanisms for reporting cyberbullying incidents” but does not mention the privacy implications of such monitoring or appropriate privacy protections, despite FPF’s comments on this issue.
“Unfortunately, the report offers little practical guidance to school officials on how to consider privacy safeguards as they implement programs to monitor threats, harden schools or train personnel,” said the authors. “Privacy doesn’t seem to have been a top concern for the Commission, even though its members heard testimony about ways to have both security and privacy.”

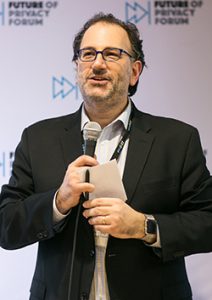 Jules Polonetsky has been CEO of the Future of Privacy Forum since its founding 10 years ago. He is uniquely suited to bring together privacy experts from industry, consumer advocacy and government. Before he joined FPF, Jules was the Chief Privacy Officer at AOL and DoubleClick, New York City Consumer Affairs Commissioner, a New York state legislator, a congressional staffer and an attorney.